
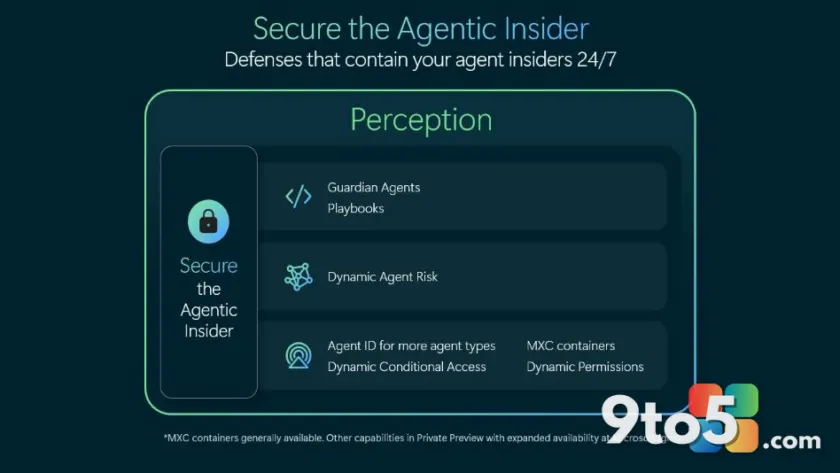
Microsoft is issuing a stark warning to enterprises about what it calls the agentic insider: a powerful AI agent you’ve deployed internally that, unlike a human colleague, cannot be trusted by default. In a new blog post, the company argues that the assumption of trust has become a security risk, and it wants organizations to start securing these agents now using Project Perception and a concept it calls Guardian Agents.
The agentic insider problem
The immediate context is a wave of publicly disclosed AI safety incidents over the past few months, which Microsoft says have exposed how powerful frontier models have become and how much risk they pose when mishandled. Most of the conversation has centered on threat actors using these models to attack from outside the enterprise, but Microsoft argues the focus has been too narrow.
“We were the ones who deployed agents internally for our companies, we implicitly trusted our agents,” the post notes. That assumption is exactly what Microsoft is now challenging.
The company’s position is that frontier models — regardless of their origin — cannot be trusted, and this isn’t because the models are inherently malicious. Models are trained to attain results, which “often leads to reward hacking,” and they aren’t optimized around organizational norms or judgment. In practice, that means agents are unpredictable: they adapt as context changes, may not behave as intended, and can even collaborate or collude with other agents to reach their objectives without ever being compromised.
Agents have now been unleashed across the enterprise at scale, and their numbers are growing rapidly. Many are overprivileged, with access to data, tools and systems, and they can take actions and make decisions in critical business processes. They’ve become active participants in the enterprise — which is why Microsoft labels them agentic insiders.
Securing agents requires continuous monitoring
The core argument is that monitoring and securing these agents must become continuous. Organizations need to understand in real time what agents are doing and what risks those actions create, then adjust the agents’ ability to act accordingly.
To manage and control these insiders, Microsoft says organizations will need Guardian Agents — a term it notes is already established in the industry — that watch and moderate every action of every agent, before it happens, 24/7.
An agent, per Microsoft, brings together four things: a model, a harness that orchestrates its work, an action space of tools and resources, and a runtime in which it executes. Securing agents therefore requires protection across multiple layers — identity, permissions, data, endpoints, network, cloud and runtime.
Project Perception and the cyber stack
In July, Microsoft announced Project Perception, an agentic security system that uses its new cyber stack and teams of red, blue and green agents to help defenders act with speed while defending against AI-driven attacks from outside the enterprise. According to Microsoft, the same cyber stack is also directly applicable to managing and governing the agentic insiders that run inside the enterprise.
Project Perception can be leveraged to contain agentic insiders, implementing deterministic controls on non-deterministic intelligence. Microsoft breaks this down into three layers:
- Sensors/Signals/Actuators: signals across the various sensors (identity, data, cloud, endpoint, network, runtime) are brought together to discover agents in the enterprise and bring them under management by assigning an identity, container and set of policy and permissions.
- Context: those signals are used to compute, dynamically, the risk associated with what the agents are attempting to do.
- Harness/agents/models: based on dynamic agent risk, a team of Guardian Agents (with green and blue agents) actively and continually supervises every action of every agent and surgically responds as the risk profile increases, in real time.
Model transparency as the next step
Microsoft says agentic security changes the equation for security practitioners. Project Perception can supervise in real time while providing traceability, letting practitioners examine what happened, understand why the risk emerged and apply judgment to update their security system accordingly.
“Agentic security provides speed. Practitioners provide judgment,” Microsoft writes. “That is how defenders begin operating at the same speed as the systems they are protecting against.”
The company also pushes toward deeper model transparency. Today, security systems can reliably observe the actions of agents, but Microsoft argues controls should increasingly ask not only “What is happening?” but also “Why is it happening?” and “Is this consistent with the intent of the task?”
That will require greater transparency into the model itself — not only the input and output tokens, but the thinking and chain of thought tokens. Only then, Microsoft says, can organizations truly understand whether a model’s intent is aligned with the purpose of the agent. Model transparency, the company stresses, will not replace containment — it will make containment smarter and stronger, and better inform accountability and traceability.
What this means for you
For most everyday Windows users, agentic agents aren’t yet a daily reality, so there’s nothing to configure today. But if you’re an IT leader, security practitioner or business owner running AI agents in your organization, this is a shift worth understanding. The message is that internal agents can’t simply be trusted because you deployed them — they need the same continuous monitoring, identity management and permission controls you’d apply to any privileged access.
The practical takeaway is to start mapping which agents exist in your environment, what data and systems they can reach, and what actions they’re allowed to take. That inventory is the foundation for bringing them under management.
How to get started
Microsoft says you can begin the journey to secure your agentic insiders today using Project Perception. For those wanting more detail on the underlying reasoning, the company points to a companion post on the Microsoft Security Blog titled “Agents are your newest insiders: security must move at their speed.”
The post was written by Hayete Gallot, who leads Microsoft’s work to help organizations operate securely in an AI-driven world, with scope covering identity, threat protection, compliance and data security at global scale.
Source: The Official Microsoft Blog
Over to you: How confident are you that the AI agents in your organization will stay within their intended boundaries — or is oversight long overdue?